A multisig wallet needs two or more keys to approve a transaction, so one stolen device cannot empty it and, in a 2-of-3 setup, one lost seed phrase cannot lock you out. For a long-term stack, a family holding or a small business treasury, that makes it the most practical upgrade over a single-key wallet.
Large losses in self-custody often come from a single point of failure: one compromised key, one misplaced backup, one rushed signature. Multisig removes that single point, and you do not need to be a security engineer to set it up.
It also fits how you rebalance. A non-custodial swap on the SwapRocket crypto exchange pays out to whatever address you give it, including your vault.
TL;DR: Multisig in 60 seconds
- A multisig (multi-signature) wallet requires 2 or more approvals to send funds.
- The most common setup is 2-of-3: three keys exist, any two can authorize a transaction.
- Multisig protects you from:
- A single device getting hacked
- One seed phrase being lost or destroyed
- A single person going rogue (teams/treasuries)
- It does add complexity, so you need a simple plan:
- Clear signer roles
- Clean key storage
- A recovery path that doesn't rely on "hope"
- When you swap assets, you can stay in self-custody: a non-custodial swap on the SwapRocket exchange needs no account and pays the output directly to your multisig vault address.
What a multisig wallet is (without the jargon)
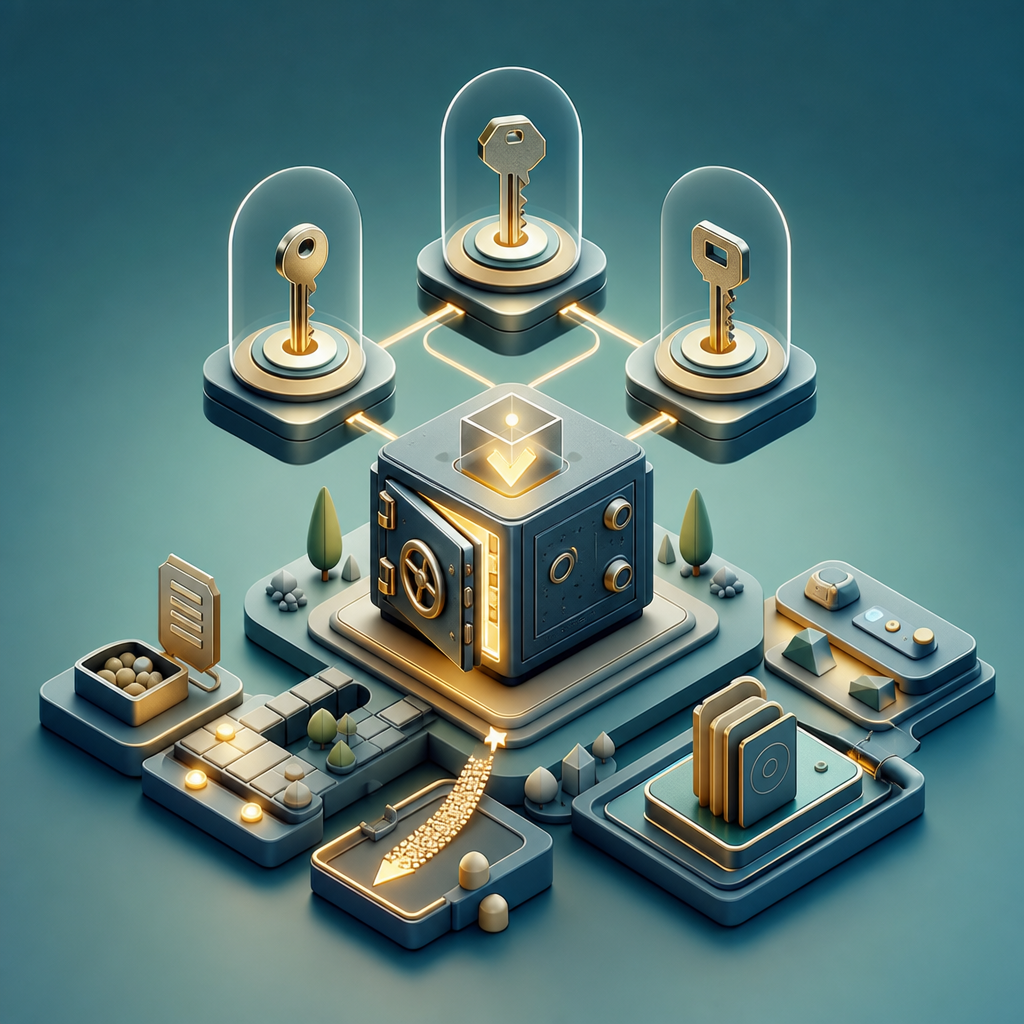
Picture a shared safe deposit box.
A normal wallet is like a box with one key. Whoever has that key can open it. If it's lost or copied, you're done.
A multisig wallet is like a box that needs two keys turned at the same time.
That's it.
In crypto terms:
- A "key" is usually created from a seed phrase (often 12 or 24 words).
- A multisig wallet sets a rule: M-of-N.
- N = total number of keys
- M = how many keys are required to approve spending
So 2-of-3 multisig means:
- There are 3 independent keys
- Any 2 can authorize a spend
- 1 key can be lost (or compromised) without losing funds
That last point is the magic.
When multisig beats a normal wallet (and when it doesn't)
Multisig is not "more secure" in every situation. It is more resilient, which matters when the stakes are high.
Multisig is a great fit if you:
- Hold enough crypto that a single-key failure would be life-changing
- Want protection against device compromise (malware, SIM swaps, remote access)
- Need shared control (partners, family, a small company)
- Want a setup where losing one key doesn't mean losing everything
A simple test: if losing one key would cost you more than you could comfortably absorb, multisig is worth the setup effort.
Multisig is not ideal if you:
- Make frequent small payments and need speed over ceremony
- Can't commit to doing a clean setup (multisig punishes "half-done")
- Don't have a safe place to store multiple backups
Multisig is a seatbelt, not a substitute for good driving.
Popular multisig setups: 2-of-3, 3-of-5, and beyond
Here's the thing most guides gloss over: the "best" multisig threshold depends on what you're defending against.
Let's keep it simple.
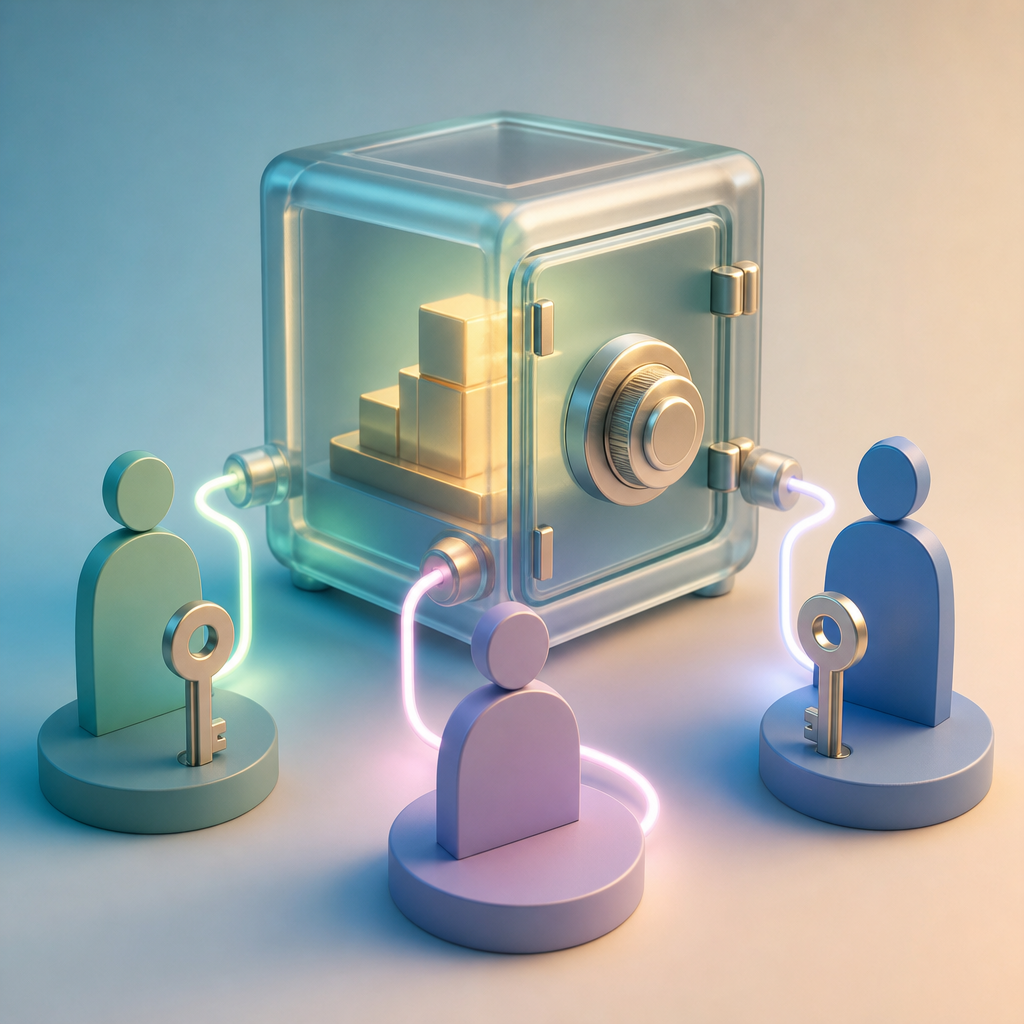
The classic: 2-of-3 multisig
This is the sweet spot for many serious holders.
Why it works so well:
- You can lose one key (fire, theft, hardware failure) and still recover.
- A thief needs two keys, not one.
- You can split keys across different locations and device types.
A common 2-of-3 layout:
- Key A: hardware wallet in your home safe
- Key B: hardware wallet in a bank safe deposit box
- Key C: recovery key stored with a trusted attorney or a second location you control
3-of-5 for teams and "too big to fail" stacks
If you're managing a business treasury, DAO funds, or a family office-style pool, 3-of-5 can reduce single-person risk.
It helps when:
- You want approvals from multiple roles (e.g., CEO + CFO + security)
- You're worried about coercion or insider threats
- You need continuity if someone becomes unavailable
Trade-off: it's more operational overhead.
1-of-2 is usually a trap
People sometimes do "1-of-2" thinking it's safer because there are two keys.
But if only one signature is needed, you're basically back to single-key security, just with extra complexity.
Quick comparison (simple on purpose)
| Setup | Best for | Biggest benefit | Biggest downside |
|---|---|---|---|
| Single-sig (1 key) | Small balances, daily spending | Simple and fast | One mistake can be fatal |
| 2-of-3 multisig | Serious holders, families | Lose 1 key and still recover | Setup + coordination needed |
| 3-of-5 multisig | Businesses/treasuries | Strong governance, continuity | More approvals, more process |
| Smart contract wallet (varies) | Power users on one chain | Flexible rules (limits, recovery) | Chain + contract risk |
A real-world multisig playbook for serious holders
Let's make this concrete.
As an example, imagine a long-term portfolio large enough that losing it would change your plans. You're not trading daily, but you do rebalance a few times a year.
Your biggest fears are boring ones:
- "What if I lose my seed phrase?"
- "What if my laptop gets compromised?"
- "What if I die and my family can't access funds?"
A sane multisig plan starts with roles.
Step 1: Decide what problem you're solving
Pick your primary goal:
- Anti-hack resilience (attacker must compromise multiple keys)
- Loss resilience (you can lose one key and still recover)
- Shared control (no single person can move funds)
You can do all three, but you need to know which one matters most.
Step 2: Choose a threshold that matches your life
For most serious individual holders:
- 2-of-3 is the best "security-to-complexity" ratio.
For businesses:
- 3-of-5 is common because it avoids a single point of failure in people.
Step 3: Separate keys by failure mode, not just location
This is the part that upgrades you from "multisig in theory" to "multisig in practice."
Don't store keys in ways that fail together.
Bad separation examples:
- Two keys on the same laptop
- Two seed backups in the same house
- Two hardware wallets ordered together, set up together, stored together
Better separation examples:
- Different device types (hardware wallet + airgapped device)
- Different locations (home + secure offsite)
- Different storage mediums (metal backup + sealed paper backup)
Step 4: Write a one-page "how to spend" policy
If you're serious enough for multisig, you're serious enough for a tiny checklist.
Your policy can be as simple as:
- Spending limit: any transaction over $X requires a second person present
- Verification: always confirm the address on a hardware wallet screen
- Timing: wait 10 minutes before signing the second key (kills impulsive mistakes)
- Change management: no key rotations without updating backups
This sounds formal, but it's really just you preventing "future you" from doing something dumb.
Key storage: the part everyone gets wrong
Multisig doesn't save you if you store keys poorly.
It can actually make things worse, because now you have more pieces to lose.
A strong key storage pattern (2-of-3)
Here is a clean setup that works for most people:
- Key 1 (Primary): hardware wallet stored at home (locked away)
- Key 2 (Secondary): hardware wallet stored offsite (bank box or trusted secure location)
- Key 3 (Recovery): seed phrase backup stored separately (sealed + documented access instructions)
And the "human layer" rules:
- Never photograph seed phrases
- Never type seed phrases into a computer connected to the internet
- Don't keep all signer devices in the same bag when traveling
The hidden risk: correlated disasters
A lot of losses come from one event taking out multiple keys.
Examples:
- House fire destroys both your "primary device" and your "backup paper"
- Flood wipes out your safe and your drawer backup
- A partner finds both seeds because they were stored "near each other"
If you remember one line from this article, make it this:
Your backups should fail independently.
Inheritance: multisig shines here
Single-sig inheritance usually means giving someone a seed phrase.
That's awkward because it's either:
- Too early (they can take funds), or
- Too late (you're gone, nobody can recover)
With multisig, you can do something more realistic:
- Your spouse holds 1 key
- You hold 1 key
- A third key is held with clear instructions (attorney, executor, or secure stored recovery)
So you get day-to-day safety and a real recovery path.
Multisig + swaps: how to move in and out safely
Here's where serious holders often slip.
They build a fortress, then casually do swaps the same way they did when they had a small balance in a hot wallet.
The safer flow is straightforward:
- Keep a small "spending" wallet for gas fees and experiments
- Keep your multisig as the vault
- When you need to rebalance, swap and send the output directly to the vault address
Why swaps matter in a multisig strategy
Multisig protects the vault, but you still need to:
- Rotate exposure (BTC/ETH/stables)
- Consolidate chains
- Move part of a holding into a different asset
Doing that without parking funds in a custodial account is the point.
On the SwapRocket exchange, a swap fits that approach:
- Non-custodial flow. You send from your own wallet and the swapped coins go to the address you give. There is no wallet connection and no account balance to withdraw from.
- No account, and no KYC for standard swaps. The licensed liquidity provider that executes the swap screens transactions and can, rarely, hold a flagged one and ask for verification.
- A typical swap takes 5 to 30 minutes, set mostly by how fast the coin you send confirms.
- 700+ assets, crypto to crypto only.
Before a planned move, open the pair on the exchange page to confirm that the asset and network you need are supported.
One multisig-specific check: make sure the vault address is on the same network as the payout. A smart contract vault exists only on the chain where it was deployed, so coins sent to the same address on another network may not be recoverable.
Example: Rebalancing BTC into ETH, then back to the vault
Let's say you want to move 10% of your BTC position into ETH.
A clean, low-drama way to do it:
- Use the BTC to ETH converter to estimate the output and sanity-check the pair.
- Start the swap on the BTC to ETH exchange.
- Set the destination address to your multisig vault receiving address.
SwapRocket uses a floating market rate, so on a larger rebalance the final amount can move slightly while your deposit confirms. For the deeper explanation of rate types, see Fixed vs floating crypto swap rates (2026 guide).
Example: Using stablecoins as a "pause button"
Sometimes the goal isn't to chase returns. It is to reduce volatility for a while.
If you're rotating into USDT or another stablecoin:
- Run something like ETH to USDT exchange
- Or quickly check a direct conversion page like SOL to USDT converter
Then send proceeds directly to the multisig address.
"How long will this take?" (the practical answer)
Multisig doesn't inherently slow blockchains down, but it does add human coordination.
For the swap itself, expect 5 to 30 minutes in a typical case, depending mostly on how fast your deposit confirms.
If you want realistic expectations and speed tips, read how long crypto swaps take.
And if a swap looks stuck, start with the SwapRocket FAQ instead of guessing.
Common multisig mistakes (and how to avoid them)
Multisig failures are rarely "crypto is broken."
They're usually process problems.
Mistake #1: Treating multisig like a magic shield
If you approve a transaction to the wrong address, multisig will faithfully execute your mistake.
Fix:
- Verify addresses on secure screens
- Use small test transactions when setting up a new destination
- Slow down the second signature (a 10-minute pause catches a lot)
Mistake #2: Storing two keys in one place "temporarily"
Temporary becomes permanent. Always.
Fix:
- Enforce a rule: keys never co-locate except during signing
- If you must travel, carry only one signer device
Mistake #3: No documented recovery plan
A common multisig regret: "We set it up, but nobody wrote down how it works."
Fix:
- Write a one-page document: wallet type, number of signers, where backups are, how to recover
- Store it securely (and ensure the right people can access it)
Mistake #4: Overcomplicating the threshold
If your setup is so strict that you can't realistically gather signatures, you've created a different kind of risk: paralysis.
Fix:
- Default to 2-of-3 for individuals
- Use 3-of-5 for teams only if roles and availability are real
Mistake #5: Mixing "hot" behavior with "cold" storage goals
If your vault is meant to be long-term storage, don't connect it to every app and site.
Fix:
- Keep a separate "transaction wallet" for experiments
- Use the vault primarily as a receiving and storage destination
How to choose a multisig wallet (what to look for)
There are plenty of multisig options across ecosystems, but your checklist stays pretty consistent.
Look for:
- Clear signing UX (you can understand what you're approving)
- Exportable configuration (so you're not locked into one interface)
- Good recovery options (documented and tested)
- Hardware wallet compatibility (for at least 2 signers)
- Ongoing maintenance (active development and security track record)
And before you commit real funds, do a rehearsal:
- Create the multisig
- Deposit a small amount
- Execute a spend using the required number of signatures
- Recover the wallet from backups (at least once)
Yes, it's tedious.
It's also how you avoid becoming a cautionary story.
A simple "serious holder" routine that actually works
If you want a practical cadence you can stick to, use this:
- Monthly: check that signer devices still power on and are accessible
- Quarterly: verify backups are intact and locations still make sense
- Twice a year: rebalance if needed (and only then do larger swaps)
- After major life events: review who controls which keys (marriage, moves, business changes)
When you do rebalance, keep it simple:
- Price-check on the pair page, for example the BTC to USDT exchange
- Swap via SwapRocket exchange
- Send proceeds directly to your multisig vault
If you're still transitioning away from custodial platforms, you'll also like this mindset shift: leaving centralized exchanges for full self-custody.
Frequently Asked Questions
What is a 2-of-3 multisig wallet?
It is a wallet controlled by three independent keys, where any two must sign before funds can move. One key can be lost or stolen without losing the funds, which is why it is the most common setup for individuals.
What happens if I lose one key in a 2-of-3 setup?
You can still spend with the remaining two keys. Use them to move the funds to a fresh multisig with three healthy keys as soon as you can, because losing a second key would lock the wallet for good.
Is multisig only for Bitcoin?
No. Multisig exists across ecosystems, but the exact implementation varies by chain and wallet type.
Does multisig mean I'm anonymous?
Multisig is about authorization, not privacy. You can pair it with privacy-friendly habits, but they're separate tools.
Can I still swap crypto if I keep it in multisig?
Yes. Many holders keep a small single-key wallet for everyday activity and a multisig vault for long-term storage. A swap can pay out directly to the vault's receiving address; spending from the vault needs the required number of signatures.
What if I need help mid-swap?
Check the SwapRocket FAQ first, or email support@swaprocket.io with your swap ID.
Related Reading
- Leaving centralized exchanges: go full self-custody
- Fixed vs floating swap rates: choose right every time
- How long do crypto swaps take? Speed tips that work
Rebalance straight into your vault
Multisig is how you stop betting everything on a single key. When it is time to rebalance, rotate into stablecoins or move between major assets, keep the same standard for the swap.
On the SwapRocket exchange you send from your own wallet and the output goes to the address you give, including a multisig vault. No account is needed and there is no KYC for standard swaps. SwapRocket is not offered to residents of the United States or the United Kingdom. To look at a pair first, start with the BTC to ETH exchange.